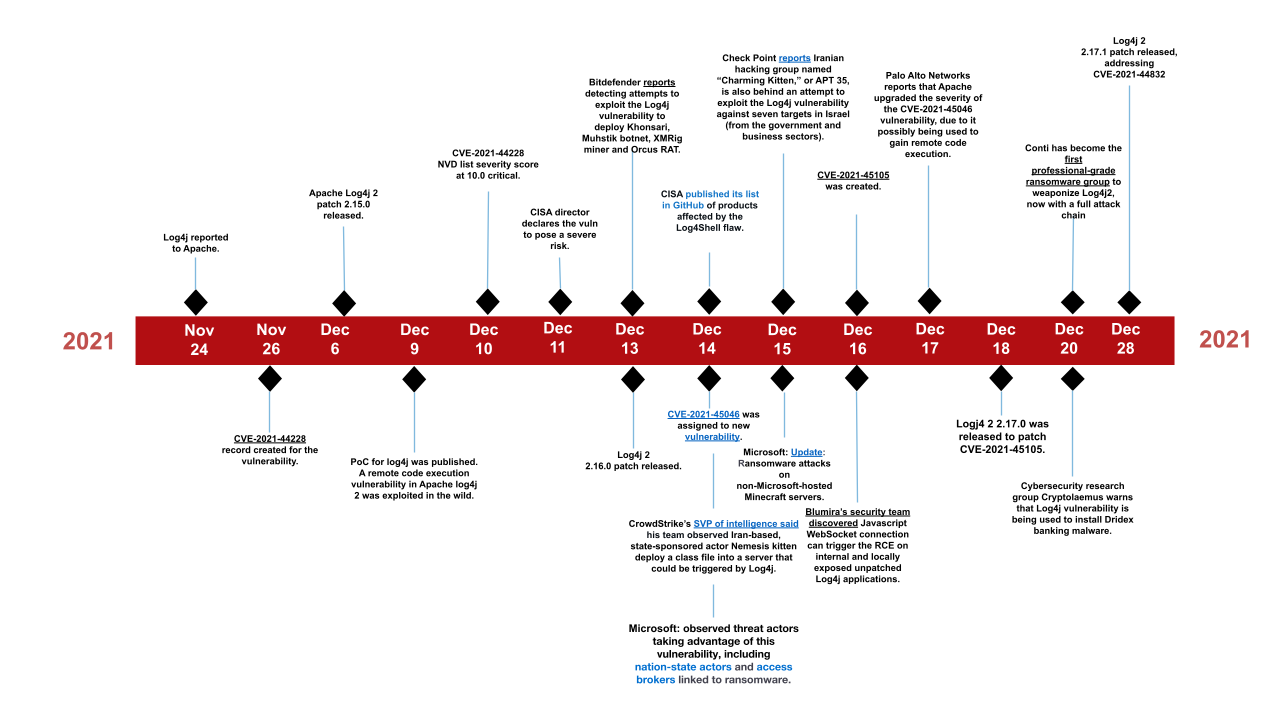
The Problem November 2021: log4shell 1/2 Correctly disclosed CVE Correctly provided patch Correctly provided package updates Yet more than 44% of companies world-wide exploited
Financial Damage More than 5M exploited servers per day 48% of networks world-wide compromised 40% rise in coin miners January 2022 Emotet Botnet revived (using log4j) Equifax received 700M in fines by the FTC Atlassian Outage March to May 2022
Why did nobody react? Existing products don't automate mitigations Existing products are glorified alert systems SIEM/SOAR Solutions don't automate Incomplete network inventory Incomplete software inventory Manual and error-prone analyst work If it's done, it's never redone again
What's wrong? Incident Response is always too late Incident Response is actually forensics, not response Forensics are manual and take too long Alerts are overwhelming and too much to deal with SIEM/SOAR doesn't make it scalable
What's wrong? Audits are manual and take too long Slow (3 months+) audits and reports No deep/live software inventory No deep/live network inventory Manual evaluation of vulnerabilities kill any advantage
What's wrong? Redundancy of maintenance work Redundancy of inventory creation Redundancy of mitigations Failure rate of outdated SBOMs Various sources of truth, none is actually correct
Features Automated network inventory Automated software inventory Automated complete audits Automated compliance reports
Features Automated incidents and mitigations Automated mitigation exchange between peers Automated zero-day detection and mitigation Automated network quarantines of infected systems
Our Products Tholian White for automated audits and compliance Tholian Blue for automated incident response Tholian Purple for automated pentests and threat intelligence Tholian Black for cyber war simulations and counter-strikes
Tholian Endpoint Agent Standalone binary with zero dependencies Can interact both defensive and offensive Generates software inventory Generates network inventory Generates user/program/configuration inventory
Tholian Endpoint Agent Analyzes program/process behaviour Analyzes kernel memory allocations Analyzes network traffic behaviour
Tholian Endpoint Agent Automated ASN/NAT and peer detection Adaptive network intrusion detection Shares incidents with peers Shares mitigations with peers Shares observed process/network/user behaviors Shares when the system seems to be compromised
OS Support FreeBSD, OpenBSD, NetBSD Debian, Ubuntu, LinuxMint, Parrot, Raspbian, PureOS Arch, Manjaro Red Hat, Fedora, Alma, Rocky, Amazon, Oracle, PhotonOS, CBL Mariner Alpine, OpenSUSE
OS Support Full Support with eBPF with Linux 4.18 and later Legacy Support via iptables, hosts, procfs
Tholian Oversight Dashboard for human interaction Schedules maintenance windows and (manual) mitigations Visualizes system inventories Visualizes network maps Automated audit reports Automated compliance reports
Our Roadmap Milestone 1 - Audits Milestone 2 - Updates Milestone 3 - Quarantines and Isolation Milestone 4 - Incidents and Mitigations Milestone 5 - Threats and Vulnerabilities Milestone 6 - Network Scans